
IAM Credential Exposure: Leveraging CTEM to Lock Down Threats
Explore how continuous threat exposure management can secure IAM credentials and mitigate vulnerabilities in the cloud.
IAM Credential Exposure: Leveraging CTEM to Lock Down Threats
With cloud environments rapidly evolving, the exposure of IAM credentials has become a pressing security concern for organizations. How can security leaders leverage continuous threat exposure management (CTEM) to effectively safeguard against this risk?
The Problem: Exposed IAM Credentials

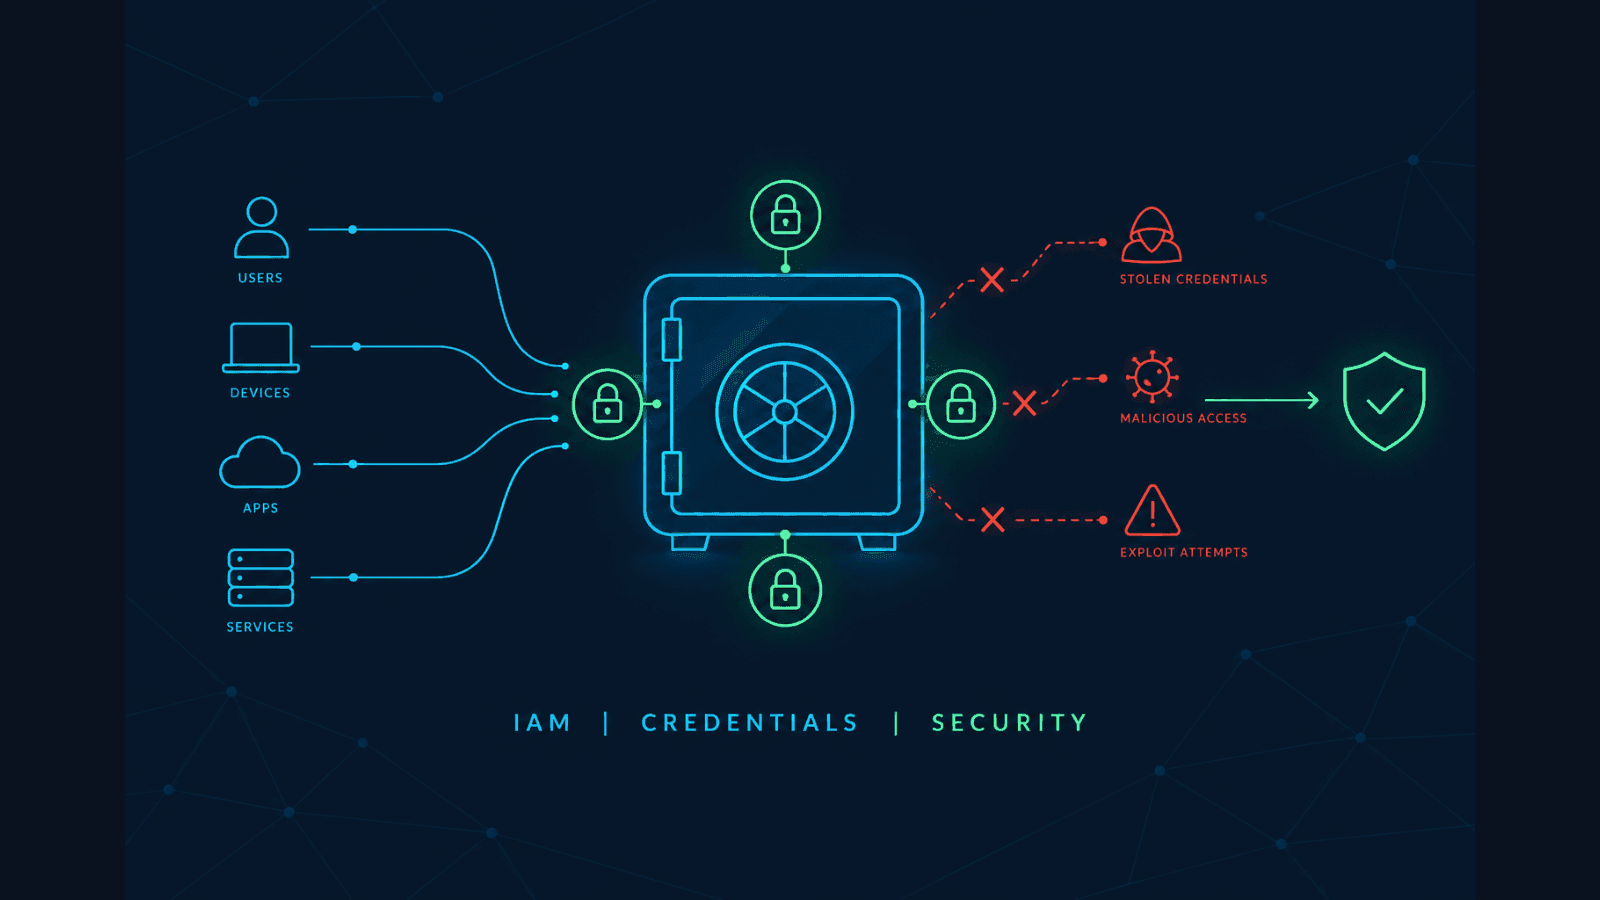
This diagram illustrates the potential risks associated with exposed IAM credentials.
When exposed, AWS IAM (Identity and Access Management) credentials can offer attackers direct access to critical cloud environments, leading to potential data breaches and service disruptions. The increasing trend of credential exposure is being fueled by several factors, such as misconfiguration, lack of security training among developers, and inadequate scanning for secrets in development tools like GitHub.
Why Legacy Approaches Fail
Traditional security measures often focus on post-exposure remediation, relying heavily on manual processes to detect compromised credentials. These methods are:
- Reactive: Only address issues after they have occurred, leaving systems vulnerable in the interim.
- Fragmented: Rely on disparate tools that do not provide a unified view of security across cloud platforms.
- Time-consuming: Prolonged detection and response times result in lost opportunities to mitigate risks.
Gartner’s reports on Continuous Threat Exposure Management highlight the urgency for teams to shift from legacy reactive strategies to proactive measures. An integrated approach is critical to minimize the attack surface and deal with IAM exposure efficiently.
The Modern Approach: Continuous Threat Exposure Management (CTEM)

This diagram outlines the process of Continuous Threat Exposure Management for securing IAM credentials.
Continuous Threat Exposure Management provides a structured way to automate and optimize IAM credential security through:
- Continuous scanning for exposed credentials and misconfigurations.
- Prioritization of vulnerabilities through exploitability and context-aware scanning.
- Integration with incident response to remediate threats in real-time, thus preventing attacks before they occur.
Trusteed’s CTEM solution emphasizes early detection, dynamic analysis, and a continuous feedback loop to keep security posture aligned with the evolving threat landscape. For instance, implementing our CTEM capabilities enables security teams to identify exposed IAM credentials swiftly and accurately.
Practical Guidance: Locking Down IAM Credentials
To fully leverage CTEM while addressing IAM credential exposure, organizations should:
- Implement Secret Scanning: Use automated tools to regularly scan repositories, including GitHub, for exposed credentials. This proactive step helps identify vulnerabilities before they can be exploited.
- Use CloudTrail Monitoring: Enable AWS CloudTrail to monitor and log API calls made with IAM credentials. Establish alerts for suspicious activity indicative of compromised credentials.
- Apply Managed Policies: Utilize AWS managed policies to restrict access based on the principle of least privilege. Regularly review policies to ensure they remain effective against current threats.
- Adopt a Continuous Security Framework: Integrate CTEM practices for executing security assessments, validating exposures, and prioritizing remediation efforts.
- Set Up Metrics for Success: Define measurable security outcomes, such as time to detect and respond to IAM credential exposure incidents, to assess your security posture over time.
Integrating IP Intelligence for Enhanced Response
Incorporating IP intelligence into your CTEM strategy can significantly reduce noise in your security operations center (SOC). By filtering relevant threat data, security teams can focus on genuine risks associated with exposed IAM credentials rather than getting overwhelmed by alerts from false positives. Trusteed's IP intelligence features are designed to provide actionable insights, helping security teams fine-tune their threat response.
Continuous Learning and Improvement
As part of an evolving cybersecurity strategy, teams must commit to continuous education and improvement about IAM threats. Conduct regular training sessions focusing on best practices regarding credential storage, management, and security hygiene. Regular feedback loops can exponentially enhance your team’s ability to handle incidents effectively.
The Attacker Already Knows…
With the ever-growing sophistication of cyber threats, understanding your vulnerabilities today may help avoid being tomorrow’s headline. By actively managing your attack surface and leveraging continuous threat exposure management strategies, you can significantly reduce the risk associated with credential exposure.
Ready to enhance your strategy for securing IAM credentials? Book a session with Trusteed and take the first step towards a more resilient security posture.